NovaCloud News
FortiGate Soc Security: Maintaining Network Visibility During Gauteng Load Shedding
Learn how 24/7 FortiGate SOC security maintains threat detection, log telemetry, and rapid response through power switchovers in Gauteng offices.
19 October 2026 · NovaCloud Africa editorial team · Cybersecurity
For business leaders across Johannesburg, Pretoria, and Sandton, managing power resilience is a daily operational reality. Uninterruptible Power Supply (UPS) units, diesel generators, and inverter banks are standard fixtures in modern Gauteng server rooms.
However, while facilities teams focus on keeping desktop screens and lights powered during grid disruptions, a critical operational vulnerability often goes unnoticed: security telemetry blindspots created during power transitions.
When a facility cuts over from municipal grid power to generator supply, brief voltage dips or delayed switch gear transfers can force network hardware into unexpected reboots. Even if primary firewalls restart within minutes, the temporary loss of syslog forwarding, interface flapping, and transient routing shifts create precise windows of exploitation.
Maintaining continuous perimeter defense requires a managed Security Operations Centre (SOC) engineered to correlate events through power cycles and maintain unbroken threat detection.
Power Instability Creates Silent Perimeter Blindspots
In a standard Gauteng office environment, a power outage triggers a rapid sequence of physical events. The transfer switch detects loss of grid voltage, signals the generator to crank, and transitions load within ten to thirty seconds.
During this window, core network stacks rely entirely on UPS battery banks. If those batteries are degraded or unmonitored, sub-second dropouts cause edge routers, core switches, and perimeter firewalls to cycle hardware states.
These brief power anomalies compromise cyber resilience in three distinct ways:
- Dropped Telemetry Streams: Firewalls that experience hard reboots lose active session tables and transient log buffers, stopping the real-time transmission of syslog events to central monitoring dashboards.
- Bypassed Identity Controls: Active Directory or Entra ID domain controllers restarting at different intervals than local network firewalls can force fallback authentication rules or unhandled policy exceptions.
- Automated Probe Exploitation: Automated threat actors continuously scan South African IP ranges. Adversaries frequently detect when a public IP drops offline and re-establishes, launching targeted intrusion scripts the moment ports reopen.
Under the Protection of Personal Information Act (POPIA), responsible parties must maintain technical and organisational measures to secure personal information against unauthorized access or loss. According to guidelines published by the Information Regulator South Africa, security measures must remain functional and monitored continuously.
A perimeter that goes temporarily unmonitored during a power cut failover presents an unacceptable compliance risk.
How FortiGate Soc Telemetry Handles Unplanned Power Cycles
Deploying a FortiGate-powered SOC addresses the vulnerability of grid instability by decoupling threat monitoring from local server availability. Fortinet hardware architecture includes local memory buffers and security fabric integrations designed to persist telemetry through temporary link interruptions.
When combined with NovaCloud’s 24/7 Security Operations Centre, FortiGate firewalls function as active telemetry nodes rather than passive loggers:
- Local Log Queuing: If WAN connections flap during an inverter transfer, FortiGate units queue critical security events locally, pushing them to the cloud-hosted FortiAnalyzer collector the moment connectivity stabilizes.
- Automated Re-Authentication: Upon reboot, FortiGate hardware enforces strict security fabric handshakes, ensuring that switch ports and wireless access points cannot pass untrusted traffic until security profiles load completely.
- Out-of-Band Heartbeats: The SOC actively monitors the heartbeat of every managed firewall. If an edge device fails to report within a defined threshold, analysts initiate immediate out-of-band checks to verify whether the cause is a routine power switchover or an active denial-of-service attack.
As documented in official Fortinet Documentation, maintaining structural fabric visibility across all network edges ensures that security policy enforcement remains identical whether operating on main grid, battery, or generator power.
Essential Security Infrastructure That Must Stay Powered
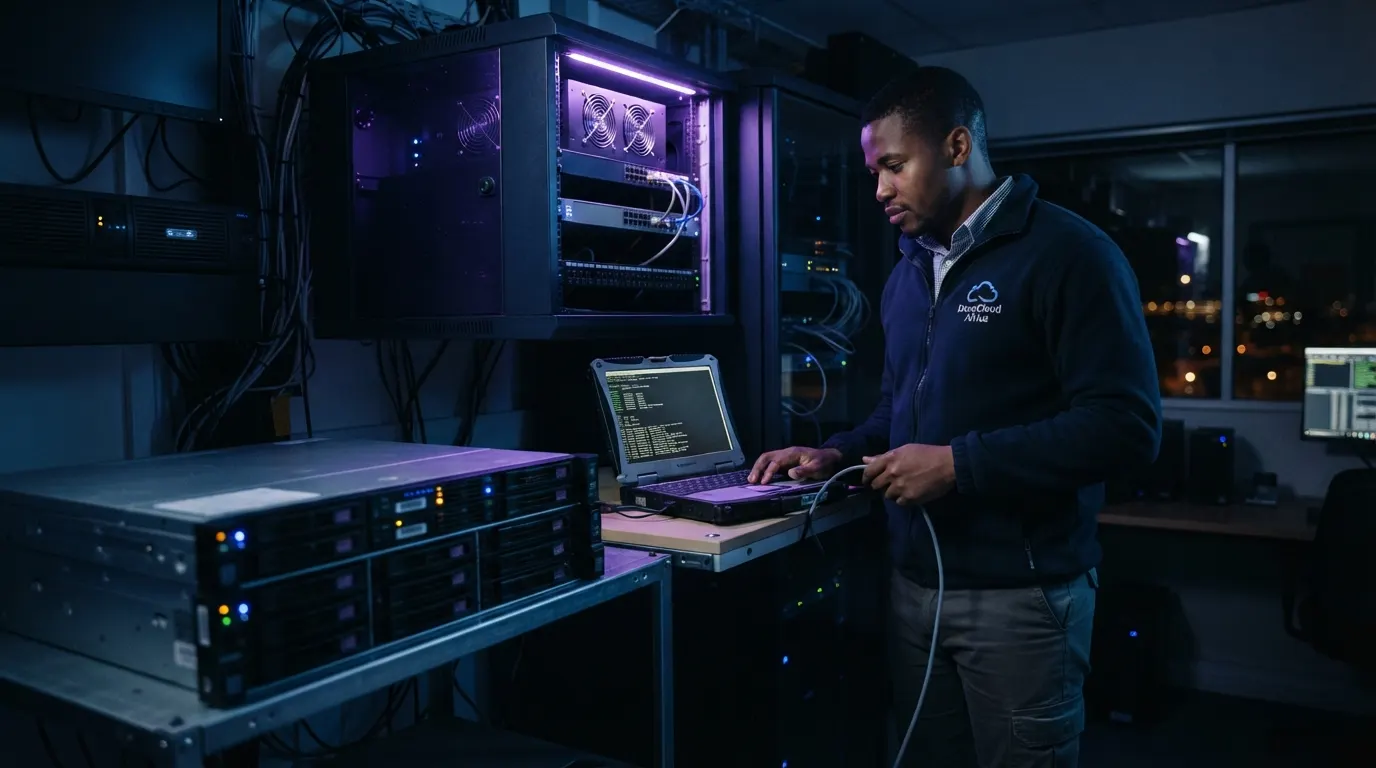
To eliminate operational coverage gaps, Gauteng decision-makers must align facility management with baseline IT requirements. When auditing office rack setups in Centurion or Sandton, specific core infrastructure components must be explicitly prioritized on dedicated UPS backbones.
- Primary FortiGate Appliance: The edge firewall must never sit on shared floor-plug circuits where desk heaters or coffee machines can trip breakers.
- Core PoE Switches: Power over Ethernet switches supporting IP security cameras, access control doors, and internal access points require calculated runtime margins to outlast generator spin-up delays.
- Primary ISP Fiber CPE: Media converters and optical network terminals (ONTs) must be tied to the same protected power rail as the firewall; powering the firewall without the CPE results in total telemetry blackout.
- Out-of-Band LTE Failover Routers: Backup cellular connectivity hardware must remain online to ensure security logs route out even if primary business fiber drops during localized power cuts.
By pairing resilient power architecture with continuous 24/7 monitoring and alerting, IT teams shift from reacting to power-induced outages to maintaining complete visibility through every grid event.
Field Experience: Securing a Midrand Logistics Hub During Weekend Grid Loss
A multi-site transport and distribution enterprise based in Midrand experienced a prolonged power failure on a Sunday evening when localized transformer maintenance coincided with municipal grid load shedding. While the site's automated generator started, a faulty relay switch caused the power feed to flap three times over a forty-minute window.
During the final power oscillation, the facility's local log server crashed due to corrupted disk volume tables. However, the edge FortiGate firewall, backed by enterprise-grade internal power regulation, successfully rebooted and established an encrypted tunnel to NovaCloud’s off-site SOC platform.
Within four minutes of the connection re-establishing, NovaCloud SOC analysts flagged an anomalous administrative login attempt originating from a foreign IP address targeting an exposed remote desktop port on an unpatched maintenance terminal. The automated brute-force attack had initiated precisely as the public IP re-registered on the local exchange network.
Because the FortiGate SOC was operating with real-time detection rules, analysts immediately executed an automated playbook: blocking the offending IP block, isolating the targeted terminal from the internal VLAN, and alerting the on-call IT director. The incident was contained before lateral movement could occur, ensuring zero impact on Monday morning supply chain operations.
Practical Steps to Fortify Soc Telemetry Against Grid Drops
Securing a Gauteng enterprise against power-induced security blindspots requires practical alignment across facilities, hardware, and operational SOC procedures. Organizations should implement five core measures immediately:
- Isolate Network Rack UPS Systems: Ensure server room racks utilize dedicated, online double-conversion UPS units separate from office floor plugs.
- Configure Managed Power Alarms: Integrate Network Management Cards (NMC) on rack UPS units into your SOC monitoring stack to receive instant alerts when on-battery states occur.
- Enforce Security Fabric Session Persistence: Verify that FortiGate firewall policies block all non-essential outbound traffic automatically until identity provider synchronization completes post-reboot.
- Deploy Redundant WAN Failover: Utilize secondary LTE or licensed microwave links so log telemetry reaches the SOC even during fiber exchange outages.
- Partner with a Managed SOC Provider: Rely on dedicated security personnel who specialize in real-time threat response across African enterprise networks. Learn more about our team and operational methodology on our About NovaCloud Africa page.
Maintaining 24/7 Threat Protection with NovaCloud Africa
Power instability is a reality of the South African operational landscape, but security blindspots do not have to be. NovaCloud Africa delivers managed FortiGate SOC services that combine enterprise hardware detection, cloud-based analytics, and local South African Standard Time (SAST) engineering support.
Whether managing single-site offices in Pretoria or multi-branch networks across Gauteng and the broader continent, our team ensures your network perimeter remains visible, monitored, and defended around the clock. Contact NovaCloud Africa today to audit your firewall telemetry resilience and establish true 24/7 SOC protection.
Protect Your Network Perimeter Through Every Power Switchover
Ensure your Gauteng office stays fully monitored during load shedding. Partner with NovaCloud Africa for 24/7 FortiGate-powered SOC detection and rapid response. Talk to NovaCloud.
Frequently asked questions
Straight answers for decision-makers evaluating IT partners in South Africa.
How does load shedding affect my company firewall security?
Power interruptions cause hardware reboots, temporary routing drops, and potential loss of local log telemetry. If firewalls reboot without active SOC monitoring, automated cyber attacks targeting newly re-established public IPs can bypass unmonitored perimeters.
What is the role of a FortiGate SOC in 24/7 threat detection?
A FortiGate SOC combines Fortinet hardware security capabilities with off-site 24/7 security analysts. It collects log telemetry, correlates threat intelligence, isolates compromised hosts, and executes rapid containment playbooks continuously.
Can FortiGate firewalls queue security logs during an internet drop?
Yes. FortiGate firewalls feature internal buffering and security fabric logging mechanisms that queue critical security events during WAN link loss, transmitting them to the central FortiAnalyzer collector once connectivity recovers.
What network hardware must be connected to a UPS during power cuts?
Essential hardware includes the core FortiGate firewall, enterprise PoE switches powering access points and security systems, primary ISP fiber CPE devices, and out-of-band LTE failover routers.
Tags
- SOC as a service South Africa
- fortigate soc
- threat detection
- 24/7 security monitoring
- gauteng load shedding cyber security
- South Africa
- Gauteng
- Centurion
- managed IT South Africa
- NovaCloud Africa